by ASCERA | Sep 22, 2026 | Blog
Every GRC vendor's demo looks impressive. Clean dashboards, green checkmarks, a slide claiming "100% audit-ready." The real test comes six months in, when you're deep in evidence collection for your SOC 2 renewal, your ISO 27001 surveillance audit, or your CMMC...
by ASCERA | Jun 23, 2026 | Blog
A recap of the joint webinar hosted by 112Cyber and ASCERA, featuring Certified CMMC Assessors Nick Graning and Jordon Darling. If you've ever stared at a blank SSP template and wondered where to start — or worse, submitted one and found out mid-assessment it wasn't...
by ASCERA | Jun 23, 2026 | Webinars
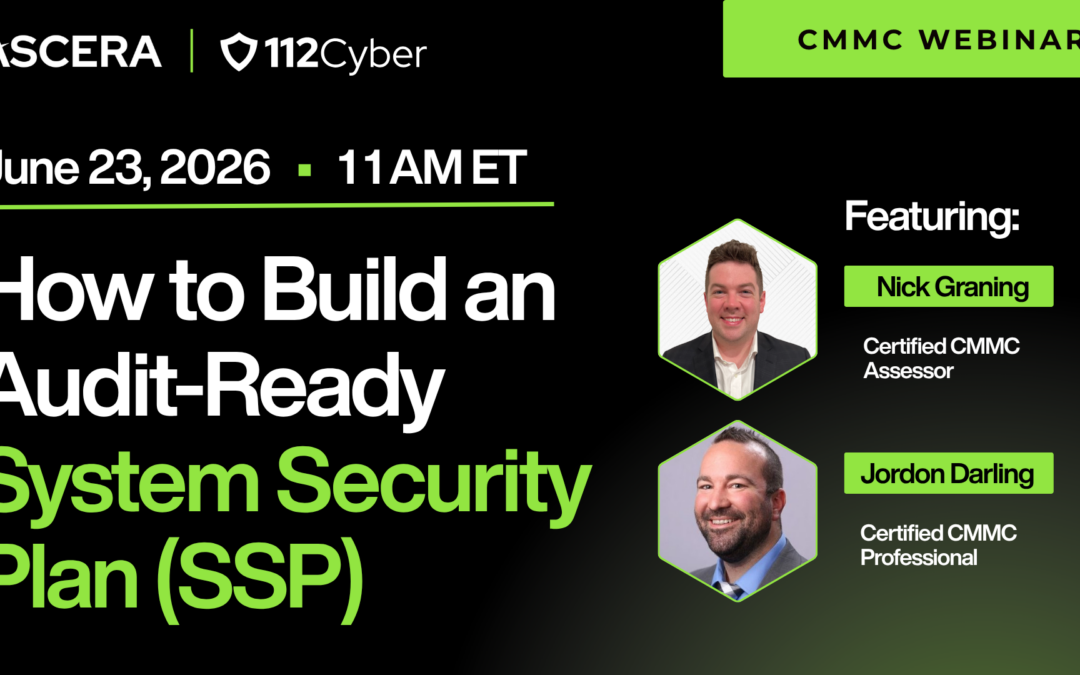
Want a written recap of the webinar? Read the full blog post → Scroll down to watch! The System Security Plan (SSP) is the backbone of every successful CMMC assessment. It's the first document assessors review, the foundation of your compliance program, and one of the...
by ASCERA | Jun 10, 2026 | Blog
If you've delivered more than a handful of CMMC assessments, you already know that a significant chunk of your time has nothing to do with cybersecurity expertise and everything to do with endurance.Copying artifact names. Pasting them into spreadsheets. Uploading...
by ASCERA | May 5, 2026 | Blog
Table of Contents What is AU.L2-3.3.4? Understanding Logging Failures Assessment Objectives Spirit of the Control NIST 800-171 R2 Discussion Common Ways to Meet It What Assessors Look For Assessment Methods Remediation Recommendation Connected Controls How ASCERA...
